
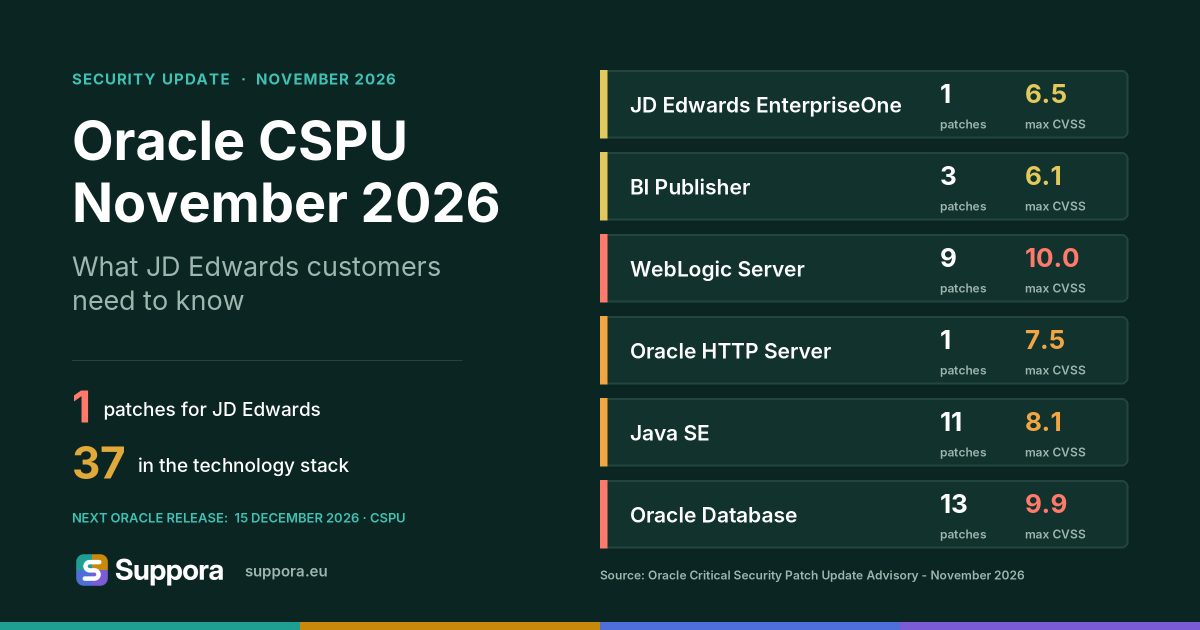
The Oracle Critical Security Patch Update for November 2026 includes important security updates for JD Edwards EnterpriseOne and its technology stack components such as Oracle Database, WebLogic Server, Java SE, BI Publisher, and Oracle HTTP Server.
What’s new
JD Edwards
This update introduces 1 new security patch for JD Edwards, with a CVSS score of 6.5, affecting the LATAM component. This vulnerability is not remotely exploitable without authentication.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-114926 | LATAM | 6.5 | No | n/a |
Oracle Database
Oracle Database receives 13 patches, with 3 vulnerabilities remotely exploitable without authentication. The highest CVSS score is 9.9 for Oracle Text (Create Session). Affected versions include 19.3-19.33 and 23.4.0-23.26.4.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-114819 | Oracle Text (Create Session) | 9.9 | No | 19.3-19.32, 21.3-21.24, 23.4.0-23.26.3 |
| CVE-2026-114848 | Oracle Text (Create Session) | 9.9 | No | 19.3-19.33, 21.3-21.24, 23.4.0-23.26.3 |
| CVE-2026-114822 | RDBMS (Create Session) | 9.9 | No | 23.4.0-23.26.4 |
| CVE-2026-72897 | RDBMS (OpenSSL) | 7.5 | Yes | 19.32-19.33, 23.4.0-23.26.4 |
| CVE-2026-115557 | RDBMS (Python) | 7.4 | Yes | 21.3-21.24, 23.4.0-23.26.3 |
| CVE-2026-89425 | Fleet Patching and Provisioning (jackson-core) | 6.5 | No | 19.3-19.33, 21.3-21.24, 23.4.0-23.26.4 |
| CVE-2026-64607 | RDBMS (Apache HttpClient) | 4.3 | Yes | 19.3-19.33, 21.3-21.24, 23.4.0-23.26.4 |
| CVE-2026-77185 | n/a | n/a | n/a | n/a |
| CVE-2026-111879 | n/a | n/a | n/a | n/a |
| CVE-2026-77421 | n/a | n/a | n/a | n/a |
| CVE-2026-77422 | n/a | n/a | n/a | n/a |
| CVE-2026-77420 | n/a | n/a | n/a | n/a |
| CVE-2026-75140 | n/a | n/a | n/a | n/a |
WebLogic Server
WebLogic Server has 9 patches, 8 of which are remotely exploitable without authentication. The highest CVSS score is 10 for TopLink Integration. Affected versions include 12.2.1.4.0 and 15.1.1.0.0.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-91569 | TopLink Integration | 10.0 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-91570 | TopLink Integration | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-91583 | TopLink Integration | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-91456 | Core | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-91470 | Core | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-91585 | TopLink Integration | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-91469 | Core | 9.4 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-9545 | Oracle Weblogic Server Proxy Plug-in for Oracle HTTP Server (curl) | 7.5 | Yes | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-91416 | Core | 5.9 | No | 12.2.1.4.0 |
Java SE
Java SE has 11 patches, all remotely exploitable without authentication. The highest CVSS score is 8.1 for the Compiler component. Affected versions include Oracle Java SE 8u511b33 and 27.0.1.0.3.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-114938 | Compiler | 8.1 | Yes | Oracle Java SE: 8u511b33-perf, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 17.0.21.0.3, 21.0.13.0.3; Oracle GraalVM Enterprise Edition: 21.3.20.0.3 |
| CVE-2026-86144 | JavaFX (libxml2) | 7.5 | Yes | Oracle Java SE: 8u511b33; Oracle JavaFX: 21.0.13, 25.0.5, 27.0.1 |
| CVE-2026-114939 | JGSS | 7.4 | Yes | Oracle Java SE: 8u511b33, 8u511b33-perf, 11.0.33.0.3, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 17.0.21.0.3, 21.0.13.0.3; Oracle GraalVM Enterprise Edition: 21.3.20.0.3 |
| CVE-2026-114940 | JSSE | 7.4 | Yes | Oracle Java SE: 8u511b33, 8u511b33-perf, 11.0.33.0.3, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 17.0.21.0.3, 21.0.13.0.3; Oracle GraalVM Enterprise Edition: 21.3.20.0.3 |
| CVE-2026-114941 | Compiler | 7.0 | Yes | Oracle Java SE: 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 21.0.13.0.3 |
| CVE-2026-114942 | Libraries | 7.0 | Yes | Oracle Java SE: 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 21.0.13.0.3 |
| CVE-2026-114943 | Hotspot | 6.5 | Yes | Oracle Java SE: 8u511b33-perf, 11.0.33.0.3, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 17.0.21.0.3, 21.0.13.0.3; Oracle GraalVM Enterprise Edition: 21.3.20.0.3 |
| CVE-2026-114944 | Core Java Libraries | 5.9 | Yes | Oracle Java SE: 8u511b33, 8u511b33-perf, 11.0.33.0.3, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 17.0.21.0.3, 21.0.13.0.3; Oracle GraalVM Enterprise Edition: 21.3.20.0.3 |
| CVE-2026-114945 | Libraries | 5.3 | Yes | Oracle Java SE: 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 21.0.13.0.3 |
| CVE-2026-114946 | Compiler | 4.8 | Yes | Oracle Java SE: 8u511b33, 8u511b33-perf, 11.0.33.0.3, 17.0.21.0.3, 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3; Oracle GraalVM for JDK: 17.0.21.0.3, 21.0.13.0.3; Oracle GraalVM Enterprise Edition: 21.3.20.0.3 |
| CVE-2026-114947 | JSSE | 3.7 | Yes | Oracle Java SE: 25.0.5.0.3, 27.0.1.0.3 |
BI Publisher
BI Publisher receives 3 patches, with 2 remotely exploitable vulnerabilities. The highest CVSS score is 6.1 for BI Publisher Security. Affected versions include 12.2.1.4.0.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-114797 | BI Publisher Security | 6.1 | Yes | 12.2.1.4.0 |
| CVE-2026-114789 | Web Server | 6.1 | Yes | 12.2.1.4.0 |
| CVE-2026-114811 | Web Service API | 4.3 | No | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
Oracle HTTP Server
Oracle HTTP Server has 1 patch, remotely exploitable with a CVSS score of 7.5 for the Weblogic Server Proxy Plug-in. Affected versions include 12.2.1.4.0.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-9545 | Oracle Weblogic Server Proxy Plug-in for Oracle HTTP Server (curl) | 7.5 | Yes | 12.2.1.4.0, 14.1.2.0.0 |
Who should care
If your JD Edwards environment uses Oracle Database versions 19.3-19.33 or 23.4.0-23.26.4, you should review the database patches.
If your JD Edwards HTML Server, AIS Server, BSSV, or Orchestrator Studio runs on WebLogic Server versions 12.2.1.4.0 or 15.1.1.0.0, these patches are relevant.
If your environment uses Java SE versions like 8u511b33, these updates are critical.
If you utilize BI Publisher 12.2.1.4.0, consider the BI Publisher patches.
If your web tier includes Oracle HTTP Server 12.2.1.4.0, the relevant patch should be applied.
What to do now
- Prioritize applying the WebLogic Server patches, especially CVE-2026-91569 with a CVSS score of 10.0, and Java SE’s CVE-2026-114938 with a CVSS score of 8.1.
- Address the Oracle Database vulnerabilities, particularly CVE-2026-114819 with a CVSS score of 9.9.
- Review your JD Edwards LATAM component and apply the patch for CVE-2026-114926.
- Coordinate with your CNC administrator and DBA to plan and test these patches in your development and pre-production environments before applying them to production.
- Oracle’s next security release is scheduled for 15 December 2026. Plan your next patch window accordingly.
Source: Oracle Critical Security Patch Update Advisory – November 2026