
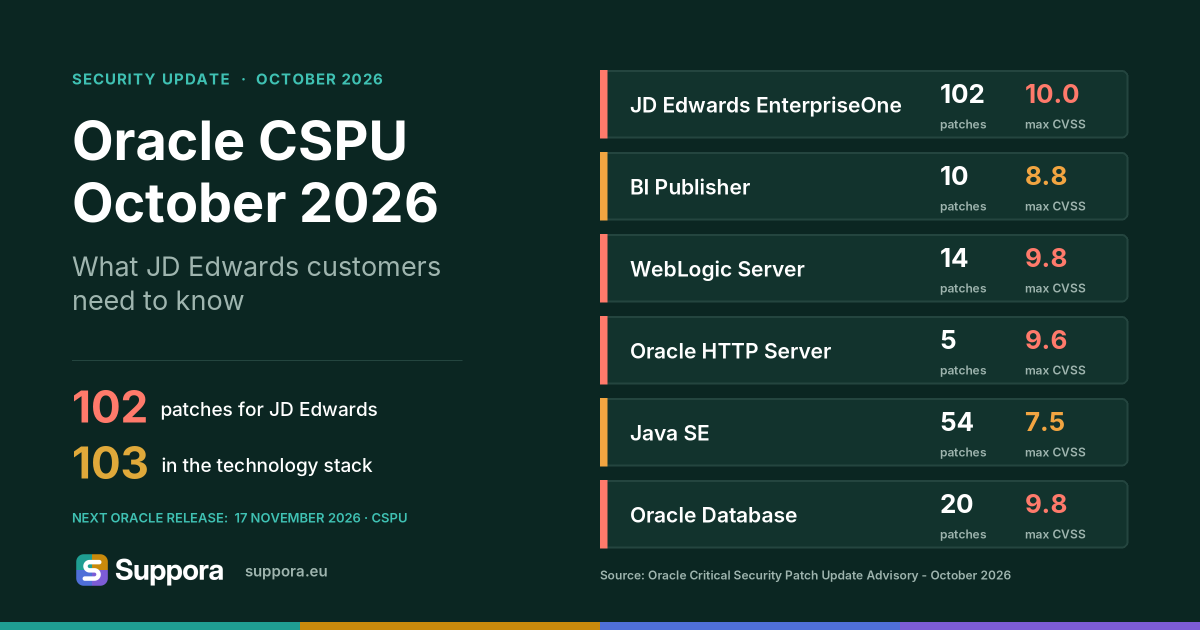
The October 2026 Oracle Critical Security Patch Update (CSPU) includes significant security patches for JD Edwards EnterpriseOne and its technology stack. Notably, JD Edwards itself has received 102 new security patches, with 44 vulnerabilities that can be exploited remotely without authentication. This overview summarizes what the Oracle CSPU October 2026 means for JD Edwards EnterpriseOne customers.
What’s new in the Oracle CSPU October 2026
JD Edwards
This update introduces 102 security patches for JD Edwards, with 44 vulnerabilities that are remotely exploitable without authentication. The highest CVSS score is 10, affecting E1 IOT Orchestrator Security (CVE-2026-91299). Affected versions range from 9.2.0.0 to 9.2.26.5.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-91299 | E1 IOT Orchestrator Security | 10.0 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2025-15467 | Enterprise Infrastructure SEC (OpenSSL) | 9.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2022-45378 | Web Runtime SEC (Apache SOAP) | 9.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91265 | Enterprise Infrastructure SEC | 9.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91305 | Installation Security | 9.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91295 | Enterprise Infrastructure SEC | 8.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91296 | Enterprise Infrastructure SEC | 8.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91303 | Installation Security | 8.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91270 | Monitoring and Diagnostics SEC | 8.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91268 | Web Runtime SEC | 8.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91326 | Installation Security | 8.8 | Yes | 9.2.0.0-9.2.26.4 |
| CVE-2026-87310 | Database and Comm SEC | 8.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91310 | Installation SEC | 8.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87313 | Interoperability SEC | 8.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91273 | Object and Env Tech SEC | 8.6 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91267 | Interoperability SEC | 8.6 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91266 | Monitoring and Diagnostics SEC | 8.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91286 | Monitoring and Diagnostics SEC | 8.2 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91269 | Enterprise Infrastructure SEC | 8.1 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91313 | Installation Security | 8.1 | Yes | 9.2.0.0-9.2.26.4 |
| CVE-2026-91271 | Monitoring and Diagnostics SEC | 8.1 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87309 | Package Build SEC | 8.1 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91287 | Enterprise Infrastructure SEC | 8.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87306 | Interoperability SEC | 8.1 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87305 | Enterprise Infrastructure SEC | 8.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91328 | Deployment SEC | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87316 | Enterprise Infrastructure SEC | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91304 | Installation Security | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91306 | Installation Security | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91311 | Installation Security | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91314 | Installation Security | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91315 | Installation Security | 7.8 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87315 | Enterprise Infrastructure SEC | 7.5 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91325 | Installation Security | 7.5 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87312 | Enterprise Infrastructure SEC | 7.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91307 | Installation Security | 7.5 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91308 | Installation Security | 7.5 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91327 | Installation Security | 7.5 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91272 | Interoperability SEC | 7.4 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91288 | Interoperability SEC | 7.4 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87314 | Interoperability SEC | 7.4 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87307 | Interoperability SEC | 7.1 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87308 | Enterprise Infrastructure SEC | 7.1 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91386 | E1 IOT Orchestrator Security | 6.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87320 | E1 Dev Platform Tech – UNIX | 6.7 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87383 | Package Build SEC | 6.7 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91383 | Monitoring and Diagnostics SEC | 6.6 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91275 | Monitoring and Diagnostics SEC | 6.6 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87387 | Homebuilder Management | 6.5 | No | n/a |
| CVE-2026-87382 | Operational Sourcing | 6.5 | No | n/a |
| CVE-2026-91285 | E1 IOT Orchestrator Security | 6.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87380 | Sales Order Entry | 6.5 | No | n/a |
| CVE-2026-91274 | Monitoring and Diagnostics SEC | 6.5 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91284 | E1 Dev Platform Tech – UNIX | 6.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91384 | Web Runtime SEC | 6.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87329 | Enterprise Infrastructure SEC | 6.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91312 | Installation Security | 6.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91329 | Installation Security | 6.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87324 | Enterprise Infrastructure SEC | 6.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87325 | Enterprise Infrastructure SEC | 6.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87321 | Package Build SEC | 6.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87318 | Enterprise Infrastructure SEC | 6.3 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87319 | Enterprise Infrastructure SEC | 6.3 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91281 | Enterprise Infrastructure SEC | 6.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91297 | Monitoring and Diagnostics SEC | 6.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91279 | Web Runtime SEC | 6.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91280 | Web Runtime SEC | 6.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87326 | Enterprise Infrastructure SEC | 5.9 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91282 | Portal SEC | 5.9 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91309 | Interoperability SEC | 5.9 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87328 | Enterprise Infrastructure SEC | 5.9 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87327 | Enterprise Infrastructure SEC | 5.9 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2025-53864 | E1 IOT Orchestrator Security (Nimbus JOSE+JWT) | 5.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87323 | Installation Security | 5.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91278 | Monitoring and Diagnostics SEC | 5.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91290 | Web Runtime SEC | 5.5 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87384 | Human Resources | 5.4 | No | n/a |
| CVE-2026-91292 | LATAM | 5.4 | No | n/a |
| CVE-2026-91455 | E1 Dev Platform Tech – UNIX | 5.4 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91298 | Web Runtime SEC | 5.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87381 | Business Logic Infra SEC | 5.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91293 | Business Logic Infra SEC | 5.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87388 | Configuration Management | 5.3 | No | n/a |
| CVE-2026-87386 | E1 Foundation | 5.3 | No | n/a |
| CVE-2026-91276 | E1 IOT Orchestrator Security | 5.3 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91277 | E1 IOT Orchestrator Security | 5.3 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91289 | Monitoring and Diagnostics SEC | 5.3 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87385 | Human Resources | 4.8 | Yes | n/a |
| CVE-2025-68161 | Web Runtime SEC (Apache Log4j) | 4.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87317 | Enterprise Infrastructure SEC | 4.8 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91283 | Web Runtime SEC | 4.3 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-91294 | Business Logic Infra SEC | 4.3 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87330 | E1 Dev Platform Tech – UNIX | 4.2 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87389 | Human Resources | 3.7 | Yes | n/a |
| CVE-2026-91291 | Business Logic Infra SEC | 3.6 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87333 | Enterprise Infrastructure SEC | 3.6 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91301 | Monitoring and Diagnostics SEC | 3.6 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-87331 | E1 Dev Platform Tech – UNIX | 3.4 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91302 | Enterprise Infrastructure SEC | 3.3 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91330 | Installation Security | 3.3 | No | 9.2.0.0-9.2.26.5 |
| CVE-2026-91300 | Web Runtime SEC | 3.1 | Yes | 9.2.0.0-9.2.26.5 |
| CVE-2026-87332 | E1 Dev Platform Tech – Cloud | 3.0 | No | 9.2.0.0-9.2.26.5 |
Oracle Database
Oracle Database receives 20 patches, with 4 remotely exploitable without authentication. The highest CVSS score is 9.8 for RDBMS (OpenSSL) (CVE-2026-75803). Affected versions include 19.3-19.32, 23.4.0-23.26.3, and 21.3-21.23.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-75803 | RDBMS (OpenSSL) | 9.8 | Yes | 19.3-19.32, 23.4.0-23.26.3 |
| CVE-2026-91563 | Oracle OLAP (DBMS_AW) | 8.8 | No | 19.3-19.32, 21.3-21.23, 23.4.0-23.26.3 |
| CVE-2026-91499 | RDBMS (DBMS_VECTOR) | 8.8 | No | 23.4.0-23.26.3 |
| CVE-2026-93569 | RDBMS (Micronaut) | 8.2 | Yes | 19.3-19.32, 23.4.0-23.26.3 |
| CVE-2026-91503 | VPD (Create Table) | 8.1 | No | 19.3-19.32, 21.3-21.23, 23.4.0-23.26.3 |
| CVE-2026-91568 | RDBMS (Create Session) | 7.7 | No | 23.4.0-23.26.3 |
| CVE-2026-101512 | RDBMS | 6.5 | No | 23.4.0-23.26.3 |
| CVE-2026-91479 | RDBMS | 6.5 | Yes | 23.4.0-23.26.3 |
| CVE-2026-91615 | Java VM | 6.3 | No | 19.3-19.32, 21.3-21.23, 23.4.0-23.26.3 |
| CVE-2026-59889 | RDBMS (jackson-databind) | 6.2 | No | 19.3-19.32, 21.3-21.23, 23.4.0-23.26.3 |
| CVE-2026-101510 | Oracle Net Services | 4.4 | No | 19.3-19.32, 21.3-21.23, 23.4.0-23.26.3 |
| CVE-2026-54399 | Oracle SQLcl (Apache HttpComponents) | 3.1 | Yes | 19.3-19.32, 21.3-21.23, 23.4.0-23.26.3 |
| CVE-2026-73964 | RDBMS (Query Optimizer) | 2.7 | No | 19.3-19.32, 21.3-21.23 |
| CVE-2026-56624 | n/a | n/a | n/a | n/a |
| CVE-2026-11824 | n/a | n/a | n/a | n/a |
| CVE-2026-49844 | n/a | n/a | n/a | n/a |
| CVE-2026-87022 | n/a | n/a | n/a | n/a |
| CVE-2026-78030 | n/a | n/a | n/a | n/a |
| CVE-2026-56741 | n/a | n/a | n/a | n/a |
| CVE-2026-71497 | n/a | n/a | n/a | n/a |
WebLogic Server
WebLogic Server is addressed with 14 patches, all remotely exploitable without authentication. The highest CVSS score is 9.8 for Core (CVE-2026-91323). Affected versions are 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, and 15.1.1.0.0.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-91323 | Core | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-83399 | Core | 9.8 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-87302 | Core | 9.1 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-87346 | Oracle Weblogic Server Proxy Plug-in for Oracle HTTP Server | 8.7 | Yes | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-83379 | WebLogic Server Proxy Plug-In for Third-Party Web Servers | 8.7 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 |
| CVE-2026-87300 | WebLogic Server Proxy Plug-In for Third-Party Web Servers | 8.7 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 |
| CVE-2026-12817 | Centralized Thirdparty Jars (Bouncy Castle Java Library) | 8.6 | Yes | 12.2.1.4.0, 14.1.1.0.0 |
| CVE-2026-41855 | Core (Spring Framework) | 8.1 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-9563 | Centralized Thirdparty Jars (Eclipse Parsson) | 7.5 | Yes | 15.1.1.0.0 |
| CVE-2023-43622 | Core (Apache HTTP Server) | 7.5 | Yes | 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2025-7962 | Centralized Thirdparty Jars (Jakarta Mail) | 7.5 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 |
| CVE-2026-91502 | Core | 7.3 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-101515 | Centralized Thirdparty Jars | 5.9 | Yes | 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
| CVE-2026-49844 | Centralized Thirdparty Jars (Apache Log4j) | 5.9 | Yes | 12.2.1.4.0 |
Java SE
Java SE receives 54 patches, with 48 remotely exploitable without authentication. The highest CVSS score is 7.5 for JavaFX (WebKitGTK) (CVE-2026-43660). Affected versions include Oracle Java SE 8u503, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, and 27.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-91484 | Java plugin | 7.5 | No | Oracle Java SE: 8u503, 8u503-perf |
| CVE-2026-43660 | JavaFX (WebKitGTK) | 7.5 | Yes | Oracle Java SE: 8u503; Oracle JavaFX: 21.0.12, 25.0.4, 27 |
| CVE-2026-91415 | 2D | 7.0 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91398 | Networking | 6.8 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91382 | 2D | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91411 | JGSS | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-101516 | Libraries | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83395 | Networking | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-87294 | Security | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91395 | Utility | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91396 | Utility | 6.5 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-101737 | Compiler | 5.9 | Yes | Oracle Java SE: 26.0.2 |
| CVE-2026-91394 | Networking | 5.9 | Yes | Oracle Java SE: 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1 |
| CVE-2026-87290 | JAXP | 5.9 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83387 | JDBC | 5.9 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91462 | JGSS | 5.9 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83374 | Security | 5.9 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-6732 | JavaFX (WebKitGTK) | 5.9 | Yes | Oracle Java SE: 8u503; Oracle JavaFX: 21.0.12, 25.0.4, 27;Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-87293 | RMI | 5.4 | Yes | Oracle Java SE: 8u503, 8u503-perf; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91385 | JavaFX | 5.4 | Yes | Oracle Java SE: 8u503; Oracle JavaFX: 21.0.12, 25.0.4, 27; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91410 | Libraries | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-87291 | Networking | 5.3 | Yes | Oracle Java SE: 21.0.12.1, 25.0.4.1, 27 |
| CVE-2026-91332 | Networking | 5.3 | Yes | Oracle Java SE: 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91451 | Networking | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91373 | JSSE | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91417 | CORBA | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83380 | JAAS | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83400 | JAXP | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91463 | JGSS | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91464 | JGSS | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91453 | Lightweight HTTP Server | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91452 | Networking | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91418 | ImageIO | 5.3 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle JavaFX: 21.0.12, 25.0.4, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83378 | Compiler | 4.8 | Yes | Oracle Java SE: 21.0.12.1, 25.0.4.1, 27 |
| CVE-2026-91487 | Compiler | 4.8 | Yes | Oracle Java SE: 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83381 | Security | 4.8 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91374 | Serviceability | 4.8 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91375 | Libraries | 4.7 | No | Oracle Java SE: 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91379 | JDK tools | 4.7 | No | Oracle Java SE: 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-46470 | JavaFX (gstreamer) | 4.2 | Yes | Oracle Java SE: 8u503; Oracle JavaFX: 21.0.12, 25.0.4, 27 |
| CVE-2026-91380 | Utility | 4.0 | No | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-87255 | Compiler | 3.7 | Yes | Oracle Java SE: 25.0.4.1, 27 |
| CVE-2026-91409 | Networking | 3.7 | Yes | n/a |
| CVE-2026-91333 | Security | 3.7 | Yes | Oracle Java SE: 21.0.12.1, 25.0.4.1, 27 |
| CVE-2026-91381 | 2D | 3.7 | Yes | Oracle Java SE: 8u503, 8u503-perf; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91334 | ImageIO | 3.7 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-87367 | JAXP | 3.7 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-87292 | Networking | 3.7 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-83376 | JSSE | 3.7 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91461 | JSSE | 3.7 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91397 | Serviceability | 3.6 | No | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91400 | Sound | 3.1 | Yes | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91402 | JavaFX | 3.1 | Yes | Oracle Java SE: 8u503; Oracle JavaFX: 21.0.12, 25.0.4, 27; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
| CVE-2026-91335 | AWT | 2.6 | No | Oracle Java SE: 8u503, 8u503-perf, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, 27; Oracle GraalVM for JDK: 17.0.20.1, 21.0.12.1; Oracle GraalVM Enterprise Edition: 21.3.19.1.1 |
BI Publisher
BI Publisher has 10 patches, 5 of which are remotely exploitable without authentication. The highest CVSS score is 8.8 for BI Platform Security (CVE-2026-91579). Affected versions are 8.2.0.0.0, 12.2.1.4.0, and 26.01.0.0.0.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-91579 | BI Platform Security | 8.8 | Yes | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91608 | Web Server | 7.5 | Yes | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91574 | BI Publisher Security | 6.5 | No | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91514 | Web Server | 6.5 | No | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91554 | Web Server | 6.5 | Yes | 12.2.1.4.0 |
| CVE-2026-91555 | Web Server | 6.1 | Yes | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91518 | BI Publisher Security | 5.4 | No | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91590 | Web Service API | 5.4 | No | 8.2.0.0.0, 26.01.0.0.0 |
| CVE-2026-91526 | Web Server | 4.7 | Yes | 8.2.0.0.0, 12.2.1.4.0, 26.01.0.0.0 |
| CVE-2026-91528 | BI Platform Security | 4.3 | No | 12.2.1.4.0 |
Oracle HTTP Server
Oracle HTTP Server includes 5 patches, with 2 remotely exploitable without authentication. The highest CVSS score is 9.6 for OSSL Module (CVE-2026-87347). Affected versions are 12.2.1.4.0, 14.1.2.0.0, 14.1.1.0.0, and 15.1.1.0.0.
| CVE | Component | CVSS | Remote without auth | Affected versions |
|---|---|---|---|---|
| CVE-2026-87347 | OSSL Module | 9.6 | No | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-87346 | Oracle Weblogic Server Proxy Plug-in for Oracle HTTP Server | 8.7 | Yes | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-91419 | OSSL Module | 7.8 | No | 12.2.1.4.0 |
| CVE-2026-91473 | Web Listener | 7.8 | No | 12.2.1.4.0 |
| CVE-2023-43622 | Core (Apache HTTP Server) | 7.5 | Yes | 14.1.1.0.0, 14.1.2.0.0, 15.1.1.0.0 |
Who should care
If you are running JD Edwards EnterpriseOne versions 9.2.0.0 to 9.2.26.5, these patches are critical. For Oracle Database users on versions 19.3-19.32, 23.4.0-23.26.3, and 21.3-21.23, these updates are essential. WebLogic Server users on versions 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0, and 15.1.1.0.0 should apply these patches. Java SE users on versions 8u503, 11.0.32.1, 17.0.20.1, 21.0.12.1, 25.0.4.1, and 27 need to update. BI Publisher and Oracle HTTP Server users on the specified versions should also take action.
What to do now
- Prioritize applying patches for JD Edwards E1 IOT Orchestrator Security (CVE-2026-91299, CVSS 10.0) and WebLogic Server Core (CVE-2026-91323, CVSS 9.8).
- Address other high-CVSS vulnerabilities such as Oracle Database RDBMS (OpenSSL) (CVE-2026-75803, CVSS 9.8) and BI Platform Security (CVE-2026-91579, CVSS 8.8).
- Review your current JD Edwards Tools Release, WebLogic, JDK, and database versions to ensure compatibility with the patches.
- Coordinate with your CNC administrator and DBA to plan and test these updates in a development or pre-production environment before applying them to production.
- Oracle’s next security release is the CSPU on 17 November 2026 – plan your next patch window accordingly.
Source: Oracle Critical Security Patch Update Advisory – October 2026
Looking for ongoing JD Edwards support? Suppora Care – JD Edwards managed services →